Your ad here
Reach the executives, lawyers and operators shaping the industry.
Advertise with usA practical privacy system for people whose names are their business: threat modelling, account hardening, removal requests, and what to do in the first hour of a doxxing incident.
For most people, a data breach is an inconvenience. For someone whose name is their business, it is an operational threat: identity documents in circulation, addresses posted in forums, private images weaponised, and a search result that follows them into every negotiation.
Privacy work is therefore not paranoia. It is infrastructure, and like all infrastructure it is cheapest to build before it is needed.
Start with a threat model
A threat model is a short, honest list of who might want your information and what they could do with it. Stalkers, extortionists, hostile family members, scrapers, rivals and ordinary criminals have different methods and different goals.
Write down the three scenarios that worry you most, then design for those. Defending against everything is impossible; defending against three specific threats is very achievable.
Separate the identities deliberately
Most professionals need at least three: a public stage identity, a business identity for contracts and banking, and a private identity used for family, medical and legal matters.
Keep them in separate email accounts, separate phone numbers if possible, and never cross-link them accidentally. A single photo reused across a public profile and a personal social account can undo years of careful separation.
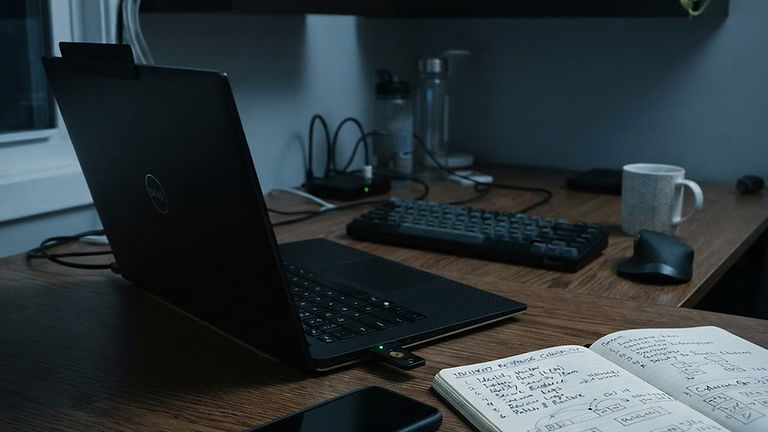
Use a password manager and unique passwords everywhere. Turn on two-factor authentication for every account that touches money or audience, and prefer an authenticator app or a hardware key over SMS, which is vulnerable to number-porting attacks.
Reduce what is already public
Data brokers aggregate addresses, relatives, phone numbers and property records, and they are the usual starting point for harassment campaigns. Most operate opt-out processes, and paid removal services automate the process if the manual route becomes a second job.
Property records and voter registrations are public in many jurisdictions and often include an address. If that is a risk for you, look into address-confidentiality programmes offered by your state, and use a mail-forwarding address for business correspondence.
Review the privacy settings on every account quarterly, and audit app permissions on your phone: location, contacts and photo access are the three that matter most.
If you are doxxed
The first hour matters more than the first week. Document everything with timestamps and screenshots before reporting. Then notify the platforms where the information was posted, using their harassment and privacy reporting routes rather than public replies.
Tell the people who need to know: your employer or booking contacts, your bank if financial details were exposed, and if there is a credible threat, local law enforcement. Save the non-emergency number before you need it.
For intimate images shared without consent, StopNCII.org creates a digital fingerprint that participating platforms can use to block distribution, and the Cyber Civil Rights Initiative publishes state-by-state guidance and a helpline. If the images involve someone under eighteen, NCMEC's Take It Down service is the correct route.

Your ad here
Reach the executives, lawyers and operators shaping the industry.
Advertise with usTakedowns and copyright
Copyright is often the fastest lever available. If you own the footage, a DMCA notice to the host is a defined legal process, and the U.S. Copyright Office publishes the rules and a directory of designated agents. Read the requirements carefully: a defective notice can be ignored, and a knowingly false one creates liability.
For search results and pages that fall outside copyright, use the platform's own removal forms and, where a platform refuses to act on a valid intimate-image request, the FTC's reporting portal for platform failures.
Device and business hygiene
Encrypt your drives. Keep offline backups. Use a password manager's shared vault for collaborators rather than sending credentials in messages. Do not store identity documents in cloud folders that sync to shared devices.
Separate business banking from personal, and use a business email for suppliers. If your accounts are compromised, that separation is what keeps a bad week from becoming a catastrophe.
When the risk is closer to home
Not every privacy threat comes from a stranger. Former partners, family members and people you have worked with can be the most persistent sources of exposure, and they often know details that a data broker never would.
Designing for that scenario looks different. It means reviewing who is on shared accounts, changing passwords and recovery questions after a relationship ends, checking which devices still have access to your accounts, and considering whether a mailing address is visible in anything you publish.
It also means being deliberate about what appears in the background of your own content: post, street signs, room layouts that reveal a building, or a window view that identifies a neighbourhood. Audiences are observant, and so are people who mean you harm.
Protecting the people around you
Your privacy plan should also cover collaborators, editors and friends who appear alongside you. Do not post someone's face, home or workplace without their consent, and expect the same in return.
If you employ or contract people, tell them what will be published and give them a way to raise concerns before publication rather than after. A single unguarded post can create a problem that takes months to unwind.
Practical takeaways
-
Write a three-scenario threat model and design for those.
-
Separate public, business and private identities with distinct emails and numbers.
-
Use a password manager, unique passwords and app or hardware-key 2FA.
-
Run a data-broker opt-out cycle twice a year.
-
Keep a printed incident checklist: document, report, notify, escalate.
-
Bookmark the safety and support resources before you need them.
Attribution: This story draws on the public sources linked at the end of the article.
About this byline
The XXXPress Editorial Desk
The XXXPress News Desk writes original reporting and context on the developments that move the adult entertainment business: regulation, payments, platform policy, workplace rules and the companies that serve the trade.
Reported and written by XXXPress editorial staff. Outside sources are attributed and linked; no sentence is copied from another publication.
Fact-checked by the desk before publication
Sources and further reading
Original reporting by The XXXPress. The links below are attributed to their publishers for verification and context; we do not host or republish their articles.
- StopNCII.org: block non-consensual intimate imagesstopncii.org
- Cyber Civil Rights Initiative: safety centercybercivilrights.org
- FTC: report platforms failing to remove intimate imagestakeitdown.ftc.gov
- U.S. Copyright Office: DMCAcopyright.gov
- EFF: Surveillance Self-Defensessd.eff.org
#privacy #cybersecurity #doxxing #takedowns #digital safety


Spotlight XXXPress: Steven Hirsch — The Visionary Who Helped Build Modern Adult Entertainment
Business & Finance · 8 min read